Thursday, 29 Oct 2026
Subscribe to AIWatcher
AIWatcher
  • Home
  • News

    OpenAI’s Berlin pitch was about owning the runtime, not the model

    By
    AIWadmin

    A one-researcher model lab ships a 10M-token coding engine

    By
    AIWadmin

    Liquid AI branches six small models off one backbone

    By
    AIWadmin

    Google gives language models a sleep cycle to remember new facts

    By
    AIWadmin

    Harvey clears the federal security bar for legal AI

    By
    AIWadmin

    Musk predicts a cull of 200 neoclouds as debt markets close

    By
    AIWadmin
  • Articles

    Google hands Oracle the keys to sell its TPUs

    By
    AIWadmin

    Airbnb drags recommendation data from two days old to twenty seconds

    By
    AIWadmin

    Android Studio opens its doors to Claude, Codex and 40 other agents

    By
    AIWadmin

    A Delaware plan would let software run companies with nobody in charge

    By
    AIWadmin

    OpenAI halves its agent pricing with a cheaper vision model

    By
    AIWadmin

    Claude for Legal now checks its own citations first

    By
    AIWadmin
  • Spotlight

    Circuit Mind puts a swarm of agents on schematic review

    By
    AIWadmin

    Upwind turns down a takeover and raises more instead

    By
    AIWadmin

    DeepMind keeps Gemini 4 Carbon behind a cyber defenders gate

    By
    AIWadmin

    Nvidia folds three speech jobs into a single open model

    By
    AIWadmin

    An inference cloud bets on rival silicon while the bears circle

    By
    AIWadmin

    Publishing staff threw a party for an AI assistant that died

    By
    AIWadmin
  • About
    • Mission
    • Services
    • Contact
  • Newsletter
  • Shop
    • All Items
    • By Category
      • Hats
      • T-Shirts
    • Cart
  • 🔥
  • Alignment
  • Classification
  • Distillation
  • Explainability
  • Hallucination
  • Legal/Compliance
  • Medical
  • NLM
  • Mobility
  • Research
  • Robotics
  • Safety
  • Startups
  • Prompt
  • Python
  • RAG
  • RLHF
  • Token
  • Vision
Font ResizerAa
AIWatcherAIWatcher
  • Home
  • News
  • Articles
  • Spotlight
  • About
  • Newsletter
  • Shop
Search
  • Home
  • News
  • Articles
  • Spotlight
  • About
    • Mission
    • Services
    • Contact
  • Newsletter
  • Shop
    • All Items
    • By Category
    • Cart
Have an existing account? Sign In
Follow US
© 2022 Foxiz News Network. Ruby Design Company. All Rights Reserved.
Alerts

A fridge hack sparked fires across European supermarkets

Attackers reached internet-exposed controllers and turned defrosters into heaters, wrecking stock across five countries.

AIWadmin
Last updated: October 16, 2026 11:26 pm
AIWadmin
ByAIWadmin
Global AI news & information.
Follow:
Share
SHARE

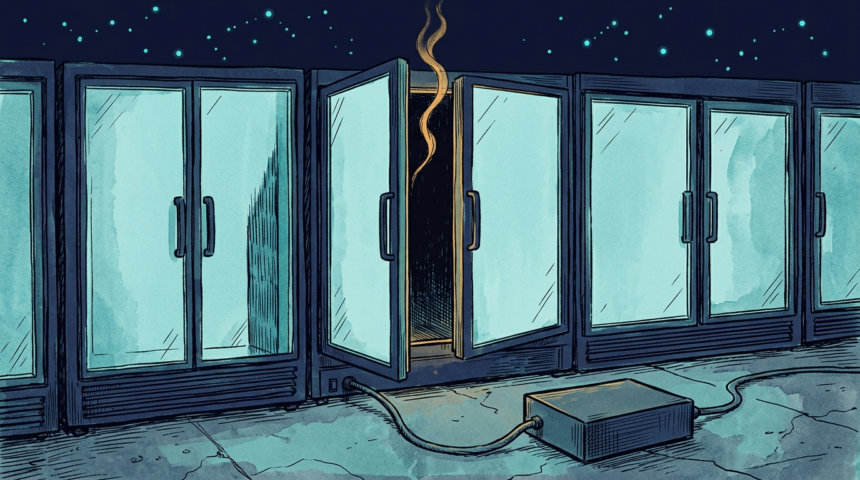
French authorities say attackers compromised the internet-connected controllers that manage store-wide refrigeration systems, then drove defrosters until cabinets reached temperatures as high as 50 Celsius. The result was spoiled inventory, smoke, and fires across supermarkets in France, Spain, Portugal, Poland, Germany and Belgium.

Contents
Basic hygiene would have stopped itNo claim of responsibility

The damage likely runs into tens or hundreds of millions of euros, according to Ars Technica. The affected controllers from Danfoss, Dixell and its parent Copeland carried critical vulnerabilities that let an attacker log in with full administrator rights. Some shipped with known default credentials and outdated firmware.

Basic hygiene would have stopped it

Researchers at Pen Test Partners laid out what was missing: the controllers were reachable from the public internet, remote access had no VPN and no IP allowlist, and third-party equipment sat on a contractor’s own connection rather than a controlled network segment.

Those are standard protections, and they were not applied. Claroty warned about exactly this class of exposure last October. CISA echoed the warning in February.

Copeland told Ars Technica the flaw affects “a discontinued, end-of-life generation of controllers.” Danfoss said the same through other outlets. Danfoss did not answer Ars Technica’s questions directly.

No claim of responsibility

Whoever did it has stayed quiet, which leaves two plausible readings. The operation could be large-scale vandalism, or it could be a state or international actor testing how much disruption a cold chain can absorb before shelves empty. Either way, the incident is a reminder that building controls are now attack surface with physical consequences.
TAGGED:critical infrastructurecyberattackEuropeIoT securityRetailVulnerabilities
SOURCES:Ars Technica
Share This Article
Email Copy Link Print
ByAIWadmin
Follow:
Global AI news & information.
Previous Article A cute robot toy leaked millions of children’s chats
Next Article Bank of America spent $200M-plus patching AI-found flaws

You Might Also Like

Alerts

A cute robot toy leaked millions of children’s chats

By
AIWadmin
Alerts

Claude products wobble again as Anthropic’s error streak hits eight days

By
AIWadmin
Alerts

RSA opens an identity layer for the agents nobody tracks

By
AIWadmin
Alerts

Pennsylvania puts AI disclosure labels on synthetic advertising across the state

By
AIWadmin
AIWatcher
Facebook Twitter Youtube Linkedin Rss

Global AI News and Information
AIWatcher is your definitive source for AI updates worldwide, from Silicon Valley to Shanghai.
Our industry coverage keeps you in the loop with the latest news and trends shaping the future of AI.

Quick Links
  • News
  • Articles
  • Spotlight
  • Events
About Us
  • Mission
  • Services
  • Contact
  • Privacy Policy
  • Legal
© 2026 AIWatcher. All Rights Reserved.